Securing the digital perimeter.
Ashwanth Saran JC — turning SIEM telemetry into decisions. Focused on threat detection, incident response, and security operations with Wazuh, FortiSIEM, SentinelOne, Sophos and Palo Alto.
About
I'm an MCA graduate currently serving as a SOC Analyst at Amvion Labs, specializing in real-time security monitoring, threat analysis, and incident response. I use SIEM platforms — Wazuh and FortiSIEM — to correlate system logs, EDR alerts, and firewall telemetry into actionable detections.
Hands-on experience spans Palo Alto and Sophos firewalls and SentinelOne EDR. Outside of work, I build threat-intel enrichment tools and automation projects — shared on GitHub and LinkedIn — to sharpen my detection and investigation skills. My focus: SOC operations, threat intelligence, and detection engineering — contributing to cybersecurity posture and incident response.
Technical Stack
Networking
- OSI & TCP/IP
- Subnetting
- VLANs
- DHCP / DNS
- NAT
- Routing
Cybersecurity
- SIEM (Wazuh, FortiSIEM)
- EDR (SentinelOne)
- Firewalls (Palo Alto, Sophos)
- MITRE ATT&CK
- Zero Trust
- Threat Intel
- Log Correlation
- Cyber Kill Chain
Languages
- Python
- PowerShell
- SQL
- HTML/CSS
- JavaScript
Tools
- Wazuh
- FortiSIEM
- SentinelOne
- Palo Alto
- Wireshark
- Nmap
- Jupyter
Systems
- Windows / Linux
- PC Assembly
- OS Deployment
- Disk Management
Service Log
Work experience
SOC Analyst
Feb 2026 — PresentAmvion Labs Pvt Ltd
- /Monitor and correlate logs from FortiSIEM and Wazuh SIEM platforms in real time to detect suspicious activity and threat patterns.
- /Configure and administer Wazuh, including rule customization, log forwarding, and integration tuning across firewall and O365 data sources.
- /Investigate and escalate potential security incidents, coordinating incident response with the security team through containment and resolution.
- /Document incidents and maintain response records to strengthen future detection and containment.
SOC Analyst Intern
Oct 2025 — Feb 2026Necurity Solutions Network Security Pvt Ltd
- /Performed initial triage of SIEM alerts using Wazuh and analyzed anomalies in network traffic.
- /Investigated malicious activity and endpoint threats using SentinelOne and Sophos EDR, correlated with Palo Alto firewall logs.
- /Deployed and maintained 800+ Wazuh agents across the client environment, contributing to detection tuning and incident response procedures.
Hardware Support Technician
2019 — 2024Freelance
- /Assembled custom PCs, installed and tuned operating systems for reliability.
- /Diagnosed BSODs and hardware/software failures across desktops and laptops.
Active Operations
Selected security engineering projects
SOC IP Analyzer ↗
Real-time investigation tool that pulls geolocation, threat reputation, and risk level for an IP by combining AbuseIPDB + VirusTotal — speeding up SOC triage.
Easy Endpoint Auditor ↗
Lightweight forensic triage tool for Windows that snapshots persistence keys, active connections, and failed auth attempts to detect malware and unauthorized access.
IP Reputation Enrichment ↗
Bulk IP reputation enrichment using free-tier threat intel APIs with Excel-friendly output and severity classification.
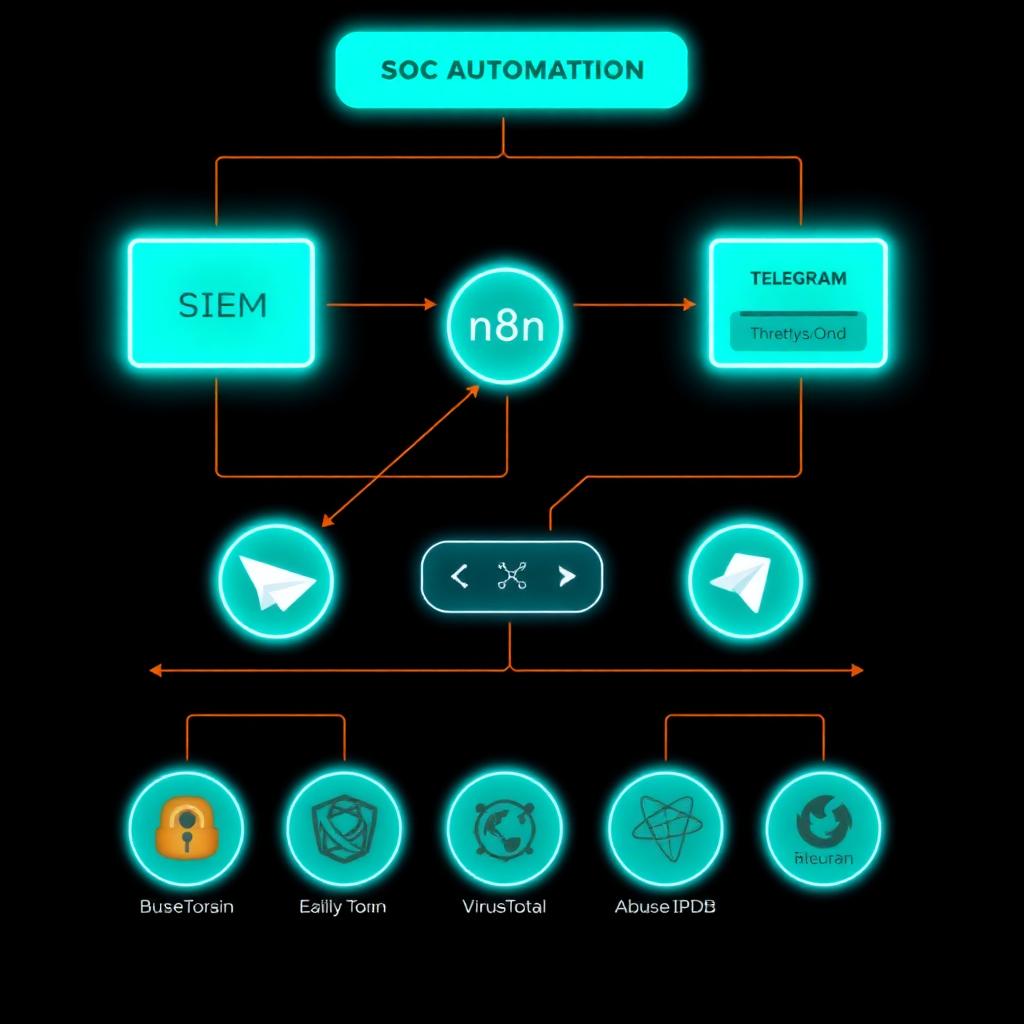
Wazuh Threat Intel Playbook ↗
Automated SOAR playbook that enriches Wazuh alerts through n8n — VirusTotal, AbuseIPDB, and GeoIP lookups on suspicious public IPs, delivering real-time context to Telegram.
CRESBOT ↗
Real-time chatbot UI for exploring college admissions, fees, and placements — demonstrates NLP concepts and interaction design.
Gender & Age Prediction ↗
Facial-image prediction system using OpenCV + CNNs. Demonstrates image processing pipeline and model deployment.
Credentials
Verified certifications and learning milestones
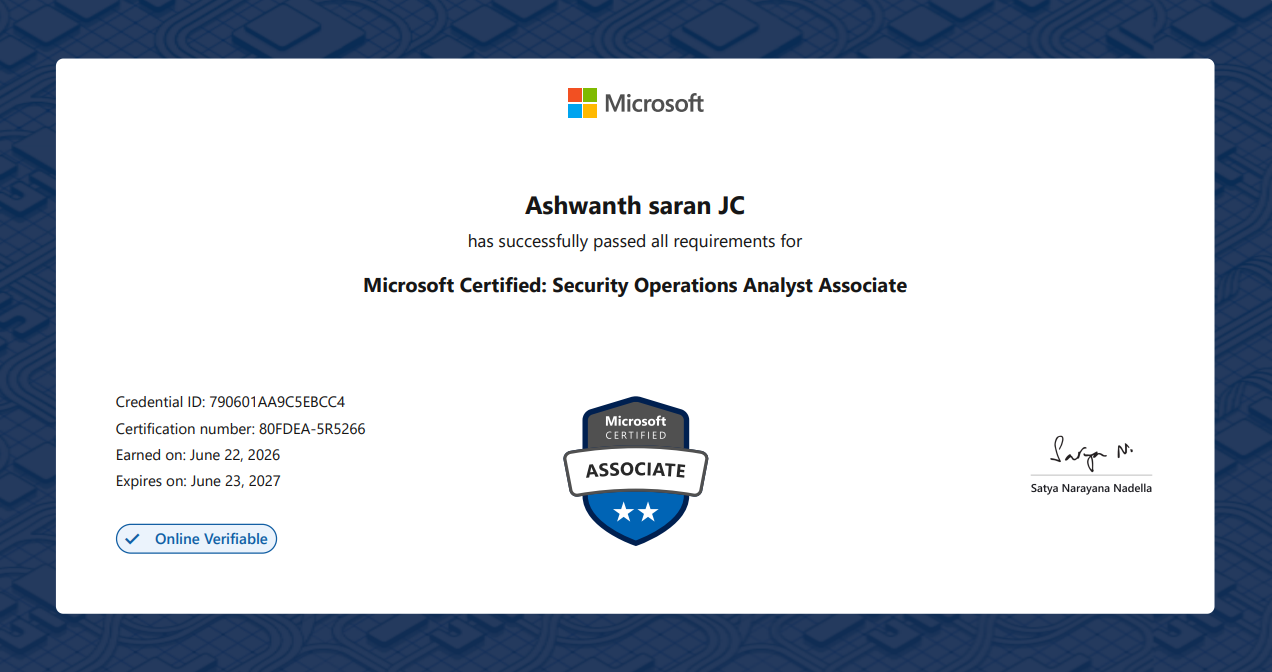
Security Operations Analyst Associate
Threat detection, investigation, and response using Microsoft Sentinel, Defender XDR, and Defender for Cloud — including KQL hunting, incident management, and SOAR automation.
Security Operations Center — SOC Analyst Essentials
Learned SOC operations, threat detection, and incident response fundamentals through Cisco's professional security training program.
Introduction to Cybersecurity Careers
Explored cybersecurity career paths, core concepts, and foundational tools used in protecting digital infrastructure.
Introduction to Generative AI Studio
Gained an understanding of Generative AI principles, tools, and applications using Google Cloud's AI Studio platform.
Pre-Security Certificate
Completed hands-on training in cybersecurity fundamentals, including networking, system administration, and foundational security concepts through TryHackMe's comprehensive pre-security course.
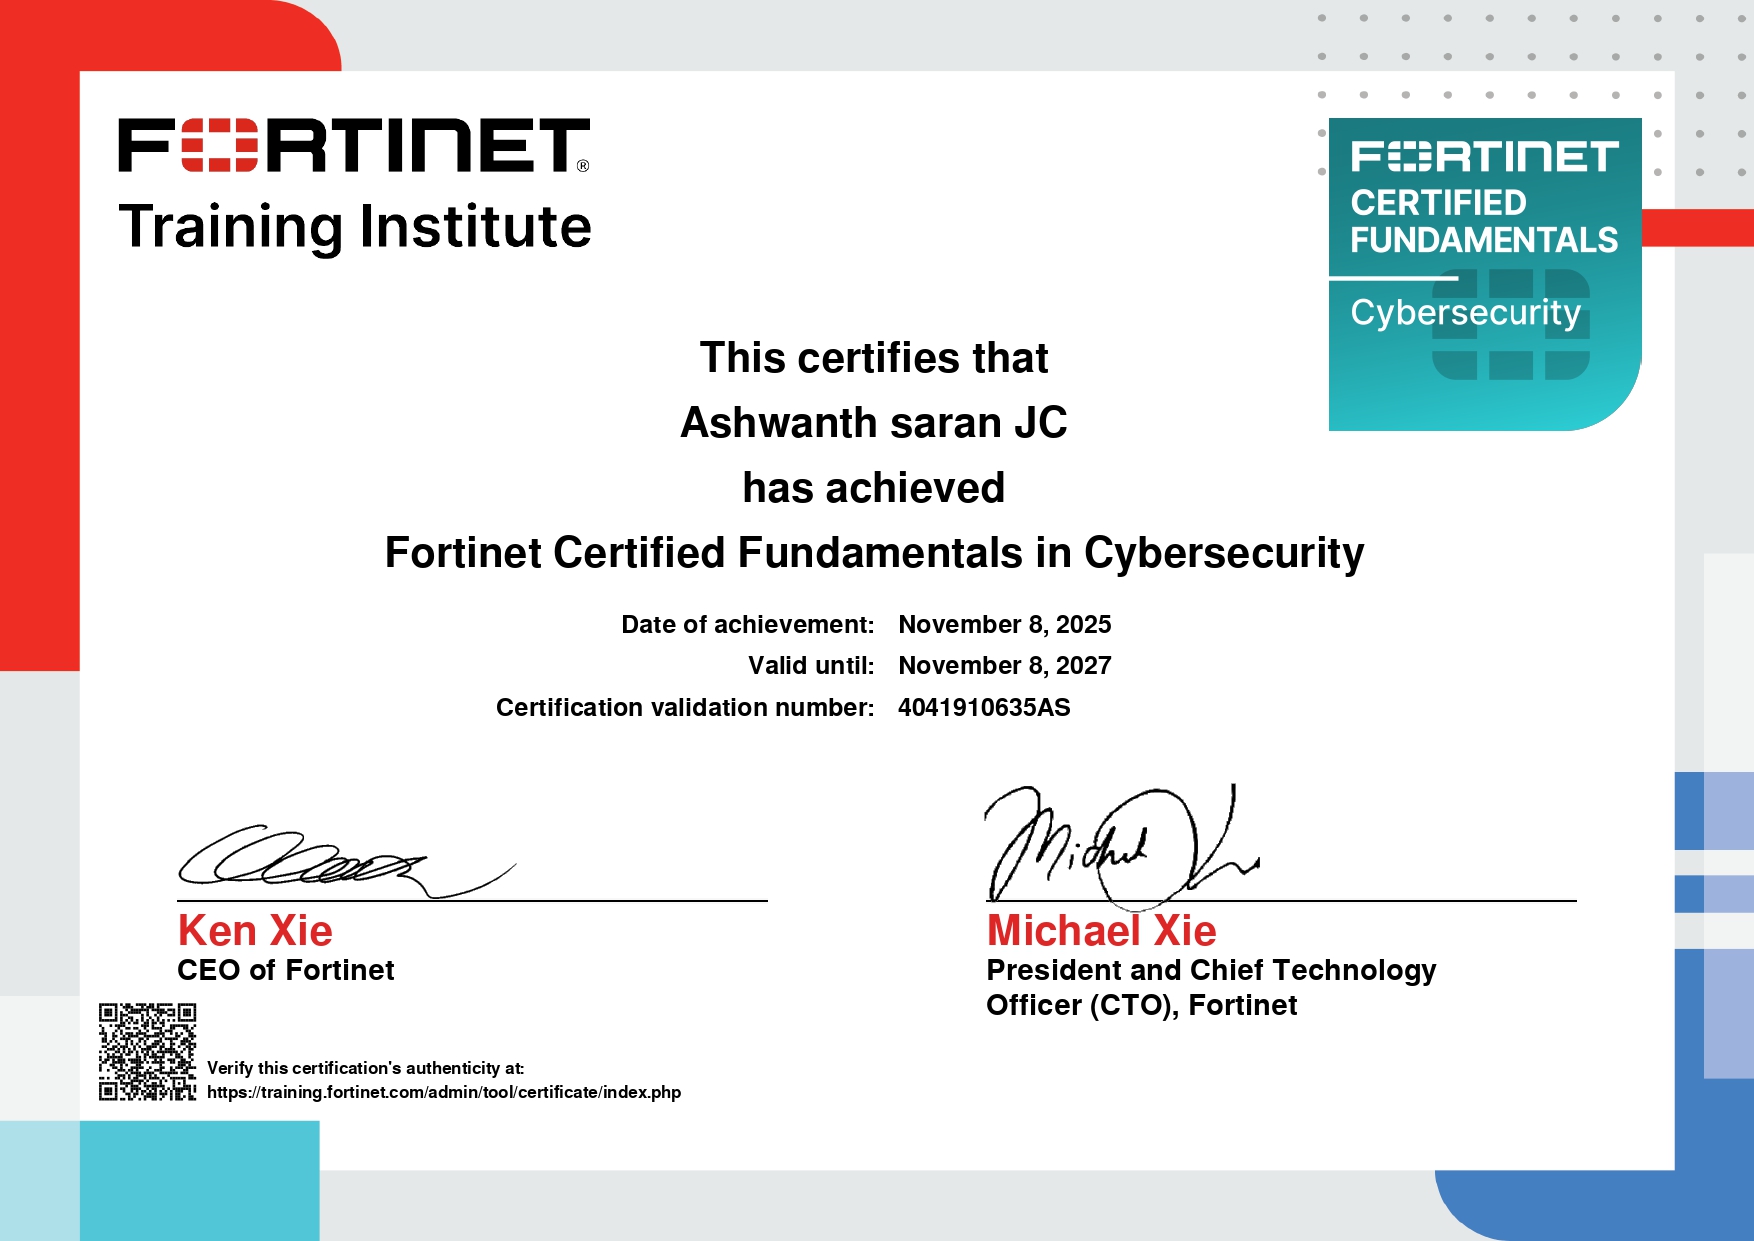
Introduction to the Threat Landscape 3.0
Earned recognition for understanding the current threat landscape, including emerging threats, threat actors, and defensive strategies through Fortinet's training program.
Achievements
Hands-on training, ranks, and recognition
ClawHavoc
Education
Master of Computer Applications (MCA)
B.S. Abdur Rahman Crescent University, Chennai
Bachelor of Computer Applications (BCA)
Vels Institute of Science, Technology & Advanced Studies, Chennai